A developer finishes a feature at 11 a.m., raises a pull request and waits. Lunch passes. The afternoon passes. The next morning, the review is still untouched. By the time comments arrive, the developer has already moved to another task and needs to mentally reload the old code before making changes. For Indian software teams working across offices, remote setups and international time zones, this seemingly small delay can quietly reduce productivity.
A healthy code review should be prompt but not rushed. For a small or medium pull request, the actual review may take 20–60 minutes, while the complete process from submitting the code to approval can reasonably take a few hours to one working day. Larger or complex changes may require one to several days, especially when multiple reviewers, security checks or architectural discussions are involved.
The better question is not simply “How fast was the review?” but whether the team received careful, useful feedback without unnecessarily blocking development.
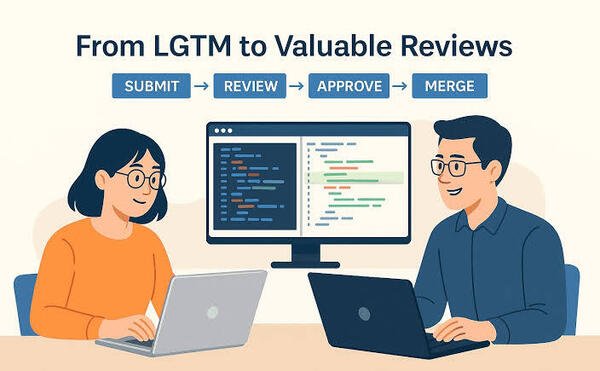
Code Review Time: Quick Overview
| Review Situation | Practical Time Expectation |
|---|---|
| Tiny bug fix | 5–15 minutes of review |
| Small pull request | 15–30 minutes |
| Medium pull request | 30–60 minutes |
| Large or complex PR | 1–2+ hours, often across sessions |
| First reviewer response | Ideally within a few working hours |
| Routine PR approval | Same day or within 1 working day |
| Complex feature | 1–3 working days may be reasonable |
| Security-sensitive change | May require additional review time |
| Emergency hotfix | Prioritised immediately |
| Very large PR | Split into smaller changes where possible |
| Review with many revisions | Multiple review cycles |
| Cross-time-zone team | Allow for working-hour differences |
How Long Should the Actual Code Review Take?
For everyday development work, reviewers should generally avoid extremely long uninterrupted review sessions.
A focused 20–60-minute session is often enough for a reasonably sized pull request.
Google’s engineering guidance recommends keeping individual review sessions to around 60 minutes or less, because the quality and attention of reviewers can decline during longer sessions.
That does not mean every pull request must be approved within one hour.
A reviewer might spend 45 minutes examining the code, request changes and return to it after the developer updates the pull request.
The complete process can therefore take several hours even though each individual review session remains focused.
How Quickly Should a Reviewer Respond?
Speed of response can be just as important as time spent reading the code.
Google’s code review guidance recommends responding promptly and generally expects reviewers to respond within one business day, although urgent work and other circumstances can affect this.
A response does not necessarily mean approval.
The reviewer might say that changes are required, ask a question or explain that a deeper review will happen later.
For many software teams, a good internal target is to provide the first meaningful response within a few working hours.
If a pull request is raised at 4:30 p.m., expecting a full review by 5 p.m. may be unrealistic. But allowing it to sit untouched for three working days without explanation can unnecessarily block progress.
Why Small Pull Requests Get Reviewed Faster
Pull request size is one of the biggest factors affecting review time.
Imagine reviewing 150 changed lines spread across four related files. The reviewer can understand the purpose, examine the logic and provide feedback relatively quickly.
Now imagine receiving 3,500 changed lines across 70 files containing database changes, UI updates, API modifications and refactoring.
The second review requires far more mental effort.
Large changes also make subtle bugs easier to miss because the reviewer must maintain more context.
This is why developers should try to create small, logically focused pull requests whenever possible.
Instead of combining database restructuring, a new checkout feature and unrelated CSS cleanup into one PR, separate them where practical.
Smaller reviews are usually faster, easier to understand and easier to test.
What Makes a Code Review Take Longer?
Complexity matters more than the raw number of lines.
A 50-line authentication change could require more careful analysis than a 500-line update to static configuration.
Reviews naturally take longer when code involves:
Security: Authentication, authorisation, payment processing and sensitive information deserve careful examination.
Database changes: Schema migrations and data transformations can have serious production consequences.
Core architecture: Changes affecting multiple services or important system components may require senior engineers.
Unfamiliar code: A reviewer who does not know the relevant module needs additional time to understand its context.
Poor documentation: If the PR description does not explain what changed or why, reviewers waste time reconstructing the developer’s intention.
Large generated files: These can make a pull request look more complicated and distract from the meaningful changes.
What Should Reviewers Actually Check?
Code review should do more than search for syntax mistakes.
Automated tools are better suited to many formatting and basic static-analysis checks.
Human reviewers should focus on questions requiring engineering judgement.
Does the implementation actually solve the stated problem?
Is the logic understandable?
Could the change introduce unexpected behaviour elsewhere?
Are error cases handled properly?
Are security and privacy implications addressed?
Are tests appropriate for the risk of the change?
Will another developer understand this code six months later?
A five-minute “LGTM” review that ignores these questions is not efficient simply because it was fast.
The objective is high-quality feedback with minimal unnecessary delay.
How Long Should Developers Wait Before Following Up?
This depends on the team’s agreed workflow.
If your organisation has a review SLA—such as first response within four working hours—follow that expectation.
Without a formal rule, a polite reminder after several working hours or by the next working day is reasonable for a normal PR.
For an urgent production fix, do not simply leave the pull request sitting in a queue. Contact the appropriate reviewer through the team’s normal communication channel.
Teams should also avoid making developers individually chase reviewers every time.
A healthy engineering process makes ownership clear: everyone should know who reviews which areas and what response time is expected.
How Many Reviewers Are Necessary?
More reviewers do not automatically produce better code.
For an ordinary change, one knowledgeable reviewer may be sufficient if company policy permits it.
Important architectural, security or cross-team changes may require two or more relevant reviewers.
Adding five people “just in case” can slow approval because everyone assumes someone else will handle it.
Code ownership rules can help automatically assign the right specialists.
For example, a payment module change might require approval from its code owner, while an infrastructure configuration update may need a DevOps or platform engineer.
Choose reviewers because their expertise is useful, not simply to increase the approval count.
Should AI Make Code Reviews Faster?
AI-assisted development tools can help reviewers identify possible issues, summarise changes and explain unfamiliar code.
Automated systems can also catch formatting problems, test failures, dependency vulnerabilities and certain programming mistakes before a human starts reviewing.
This can reduce repetitive work.
However, AI-generated comments should not automatically replace human engineering judgement for important production code.
An AI tool may identify a suspicious pattern without understanding the full business requirement, or it may miss a problem that becomes obvious when considering how customers actually use the feature.
The most effective workflow uses automation to remove routine noise so humans can focus on architecture, correctness, security and maintainability.
How Teams Can Reduce Code Review Time
Start before the pull request is created.
Developers should keep changes focused and provide a clear description explaining what changed, why it changed and how it was tested.
Run automated tests, linters and relevant checks before requesting human review.
Avoid sending obviously unfinished work for final approval.
Teams can also define a practical review expectation—for example, routine pull requests should receive an initial response within the same working day.
If a change is too large to review comfortably in one sitting, consider splitting it.
For distributed Indian teams working with colleagues in the US or Europe, account for time zones when selecting reviewers. A PR submitted after another team’s working hours cannot reasonably receive an immediate response.
Most importantly, measure review delays. If developers routinely wait two days for a 20-minute review, the problem is probably not coding complexity—it is the team’s workflow.
FAQs
Q1. Is 30 minutes enough for a code review?
A. For a small or medium, well-structured pull request, 30 minutes can be sufficient. Complex security, architectural or database changes may require considerably more time.
Q2. How long should a pull request wait for review?
A. Routine PRs should ideally receive a meaningful response within a few working hours or one business day. Teams can establish their own response-time expectations based on workload and project requirements.
Q3. Why do large pull requests take so long to review?
A. Large PRs increase cognitive load and make relationships between changes harder to understand. Breaking work into smaller, logically focused pull requests generally makes reviews faster and more reliable.
Q4. Should code review happen before or after testing?
A. Developers should normally run relevant automated tests and basic quality checks before requesting final human review. Reviewers can then focus on correctness, design, security and maintainability instead of easily detectable problems.